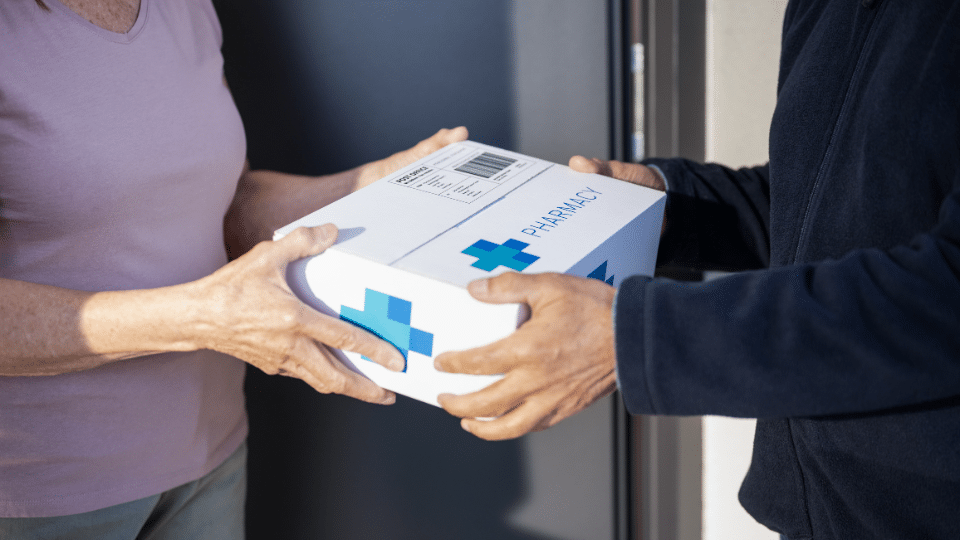
HIPAA requirements for medical courier services are determined by Business Associate status, which applies to every medical courier organization that transports Protected Health Information on behalf of a covered entity, creating obligations under the HIPAA Security Rule and any applicable HIPAA Privacy Rule and HIPAA Breach Notification Rule standards that govern the functions the courier performs. There is no delivery arrangement or operational structure that removes a medical courier from Business Associate status, and regulators treat medical couriers as having operational access to PHI as an inherent feature of their service. A Business Associate Agreement must be executed with each covered entity before any PHI is handled, the organization must implement HIPAA Security Rule safeguards across its operations, and every member of the workforce whose activities involve PHI must receive documented HIPAA training. Medical couriers in Texas must also comply with mandatory training in HB 300 and related state medical privacy laws.
All courier staff must receive security awareness training, and staff whose activities bring them into contact with PHI must receive HIPAA training on the applicable regulatory standards. Annual HIPAA training is the accepted industry best practice for maintaining a workforce that applies compliance obligations correctly in the field. The HIPAA Journal’s HIPAA Certification for Medical Couriers is an online course satisfying HIPAA training requirements regarding HIPAA rules and regulations with certification on passing tests.
Medical couriers who transport specimens, chemicals, or other regulated materials require training under three OSHA standards in addition to HIPAA training: the Bloodborne Pathogens Standard, the Hazard Communication Standard, and the Personal Protective Equipment Standard. HIPAA training governs the handling of PHI on labels, requisition forms, manifests, and dispatch systems. OSHA training governs the physical hazards of the materials the courier carries. The two sets of obligations apply at the same time and are satisfied by separate training.
 PJ Murray is the founder and publisher of The HIPAA Journal. He has more than 10 years of experience writing about HIPAA, healthcare compliance, patient privacy, and the protection of medical records. Through The HIPAA Journal, PJ helps healthcare organizations, business associates, and their employees better understand HIPAA regulations, reduce compliance risks, and strengthen the safeguards used to protect patient information.